Email Security
Phishing and malware filtering, attachment protection and domain authentication configuration. Protection for business communication and Microsoft 365.
Email, endpoints, identities, cloud and AI. We connect prevention, EDR/XDR, SOC operations and data protection with a practical response and recovery plan.
From the first email to recovery after an incident: complementary controls with defined ownership and procedures.
Phishing and malware filtering, attachment protection and domain authentication configuration. Protection for business communication and Microsoft 365.
Behavioural prevention, hardening and device protection. EDR to detect and investigate suspicious activity on endpoints.
XDR, MDR and SOC: event correlation, triage and coordinated response. 24/7 SOC coverage through a partner service within agreed scope.
Inventory, vulnerability assessments and system and application updates. Risk-based prioritisation, maintenance windows and post-deployment checks.
Layered defence: reduce the attack surface, detect, contain and retain recovery copies separate from production.
Backup for servers, workstations, virtual environments and Microsoft 365 as designed. Encryption, access control and recovery checks.
Restart plans, service priorities and recovery environments. Agreed RPO/RTO targets, failover exercises and return-to-production procedures.
Data classification, permissions and sharing rules. DLP controls to reduce exposure of sensitive information through business channels and tools.
Safer use of GenAI tools, protection of data in prompts and controlled access for agents and integrations. Governance, visibility and permission reviews.
Technology collects signals. Processes and specialists turn them into decisions and authorised action.
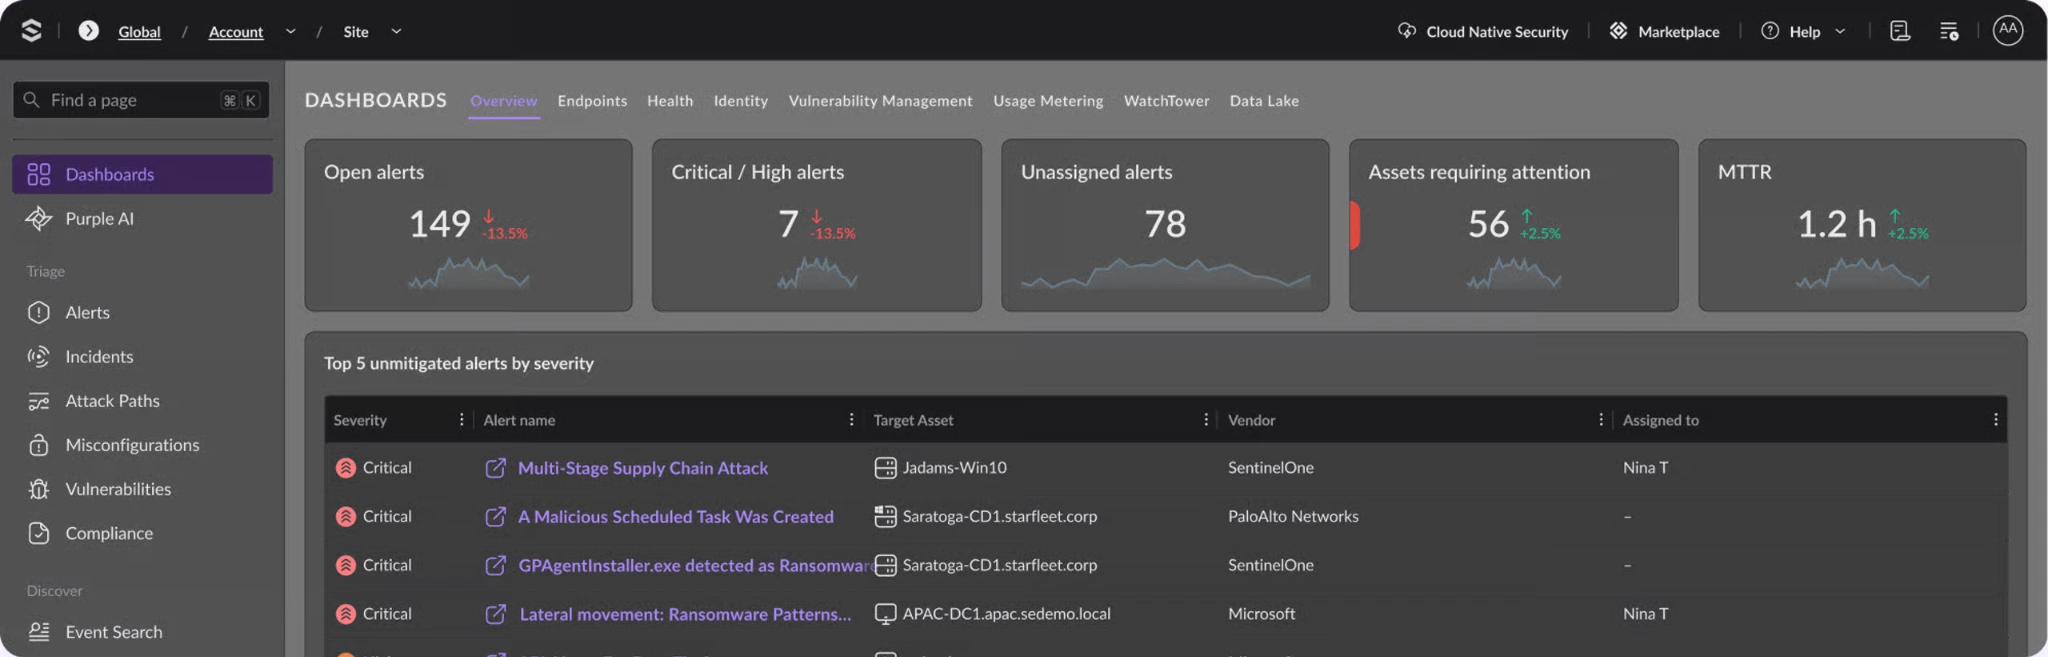
Visibility and response on individual endpoints.
Endpoint, identity, cloud and other signals connected for investigation.
A managed service adding specialist analysis and response.
Monitoring and management through a partner SOC service. Data sources, intervention coverage, containment, escalation and SLAs are defined for the contract; service scopes differ.
Encrypted recovery copies separate from operational systems. Where supported, immutability or WORM/Object Lock prevents changes and deletion during the configured retention period.
Region, access and service selection. With Cove we use provider infrastructure with declared certifications including ISO 27001 and SOC 2 Type II, reviewing the applicable scope.
Define what recovers first, acceptable data loss (RPO) and the recovery time objective (RTO). Recovery exercises validate the plan; a backup alone is not the whole recovery process.
Provider certifications are not certifications of Intellope. Immutability, retention and recovery depend on product and configuration. Cove Fortified Copies uses provider-managed isolated copies; this differs from customer-configured S3 Object Lock.
N-able / Cove Security Guide ↗Bring policies and oversight into new workflows: which data may enter AI tools, who can access it and which actions agents may perform.
We design dedicated infrastructure for technology platforms and demanding environments: tenant separation, controlled administrative access, segmentation, encryption and independent recovery.
Build protection around your risks by connecting prevention, detection, response and recovery.
Protected identities, updates, backups and secure configurations.
EDR/XDR endpoints, Microsoft 365 protection and network segmentation.
Event analysis, vulnerability assessments and security reviews.
Monitoring through a partner SOC service, analysis and response coordination within the agreed scope.
24/7 SOC coverage is an agreed service: monitored systems, escalation, intervention and SLAs are defined in the contract.
We support improvement and preparation; certification is issued by the relevant independent certification body.
Networks, identities, endpoints, configurations and access.
Gap assessments, vulnerability analysis and testing within authorised scope.
Technical and organisational support for readiness and audit evidence.
Response plans, backups, recovery exercises and clear ownership.
Yes. We start with your existing environment and review access, dependencies and integration options before proposing changes.
After an initial discussion we define the work, expected outcomes and responsibilities. Timing, support conditions and costs are agreed for the project; this page is not a quote or SLA.
Complete IT management or support for your team.
Explore the serviceSolid foundations for systems that need to work.
Explore the serviceModules, integrations and licences are selected for the project. Email security, DLP and other controls may require dedicated products; one platform does not bundle every capability.
We connect expertise, people and technology around your project.
Contact us about a project, a question or an IT issue.
Do not send passwords, access codes or sensitive data.
You can also email [email protected].